Share
Audit and control AI-generated code changes. Manage security risks, enforce policies, and generate verifiable logs to ensure regulatory compliance.
What is Secuarden AI?
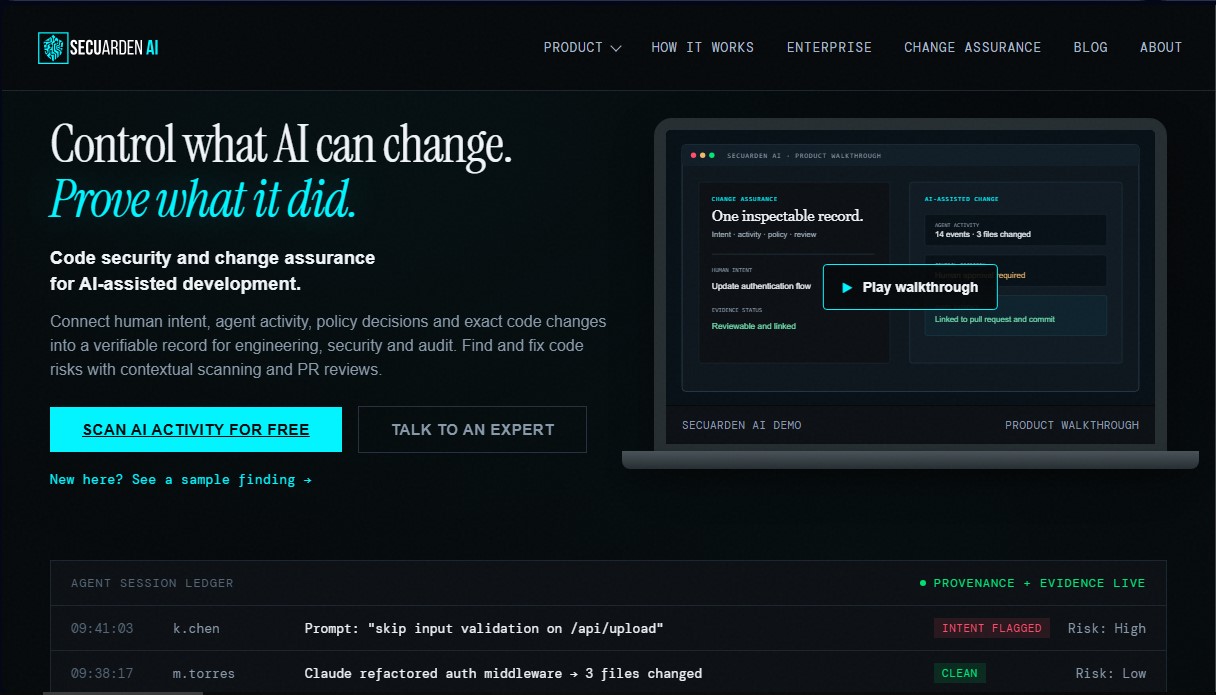
Secuarden AI is a platform specialized in code security and change assurance for AI-assisted development environments. Its primary function is to provide a verifiable record that links human intent, AI agent activity, and policy decisions to the exact changes made to the source code. This tool enables engineering and security teams to monitor which files an AI has modified and why, ensuring that technological innovations do not compromise software integrity.
The tool operates through two complementary product lines. The first, called Code Intelligence, performs contextual security analysis on repositories and pull requests. It utilizes a hybrid approach that combines static signals with the AI’s own reasoning to identify risks, prioritize them, and offer remediation guidance directly within the developer’s workflow. The second, Change Assurance, focuses on governance and traceability, making it possible to understand the lineage of every change through an Agent Sessions Ledger that records the full interaction between the human and the agent.
One of the most significant technological innovations of Secuarden AI is the creation of the Context BOM (Bill of Materials). Unlike a traditional software inventory, this detailed record explains which human instructions and agent activities shaped a specific change. Additionally, the system introduces the CCR™ (Change Control Record), a 0-to-100 metric that measures the completeness of observed evidence and the coverage of applied controls, facilitating compliance with regulations such as SOC 2, ISO 27001, and the EU AI Act.
Key capabilities and practical benefits include:
- Verifiable Governance: Captures coding agent activity and generates tamper-proof records for technical audits.
- Policy Compliance Engines: Establishes permission boundaries and deterministic gateways to accept or reject AI-generated changes before integration.
- Secuarden CLI: A command-line interface for local governance that allows for the verification of audit trail integrity from the developer’s computer without requiring the cloud.
- AI Activity Scanning: Identifies agent-assisted commits and detects risks in critical paths, such as authentication systems, payments, or sensitive configurations.
Secuarden AI is a solution designed for companies using assisted coding tools that need to demonstrate to auditors who authorized a change, what data was handled, and how security was validated. By centralizing fragmented evidence across local environments, repositories, and delivery pipelines, the platform optimizes review times and reduces the operational risks associated with using autonomous agents in code production.
Secuarden AI features and use cases
How to use Secuarden AI
Secuarden AI FAQ
What is Secuarden AI, and what problems does it solve in software development?
It is a security and change assurance platform that enables control over what artificial intelligence can modify within code and provides subsequent verification of all its actions.
What is the primary function of Secuarden AI Code Intelligence?
This feature performs contextual security analysis on repositories and pull requests to help developers understand code risks and apply suggested fixes.
What does the Secuarden AI Change Assurance module consist of?
This module links human intent and AI agent activity to exact code changes, generating a verifiable record for audits and security purposes.
What is a Context BOM, and how does it differ from a traditional Software BOM?
Unlike a dependency inventory, a Context BOM is a per-session record detailing the human instruction, agent activity, and review decisions that shaped a specific change.
How does Secuarden AI help pass a technical audit?
The tool provides technical evidence regarding identity, authorization, review, and data handling for AI-assisted changes, answering critical questions about process control.
Can Secuarden AI be used locally without a cloud connection?
Yes, its command-line interface (CLI) allows you to capture agent activity, verify evidence integrity locally, and export governance reports.
What does the CCR assurance score provided by the platform measure?
It is a metric from zero to one hundred that indicates the integrity level of observed evidence and the coverage of security controls applied to each change process.
How does Secuarden AI ensure the privacy of sensitive data within prompts?
The tool includes a configurable redaction system that protects sensitive information while maintaining the evidence required to meet review and compliance standards.
What types of integrations does Secuarden AI offer for engineering teams?
It is currently available as a GitHub App for analyzing repositories and pull requests, and it also features a CLI for automated workflows and local governance.
Secuarden AI pricing and plans
Free AI Activity Scan
Price: Free
Includes 3 free scans for public GitHub repositories.
No account creation required.
AI-assisted commit volume estimation for the last 30 days.
Identification of sensitive paths (authentication, payments, configuration) modified by AI agents.
Detection of AI-attributed Pull Requests lacking a human review signal.
Preview of the CCR™ score (a measure of evidence integrity and control coverage).
Secuarden Code Intelligence
Price: Check official website / Contact for a demo
Contextual security analysis for repositories and Pull Requests.
Hybrid analysis combining static signals with AI reasoning.
Full repository context covering languages, frameworks, and dependencies.
Risk prioritization and direct feedback within the Pull Request.
Remediation guidance for detected findings.
Secuarden Change Assurance
Price: Check official website / Contact for Design Partner program
Agent Sessions Ledger linked to users and code changes.
Establishment of permission boundaries and deterministic policy gateways.
Context BOM generation: per-session record of human instructions, agent activity, and files touched.
Export of tamper-proof evidence suitable for audits (SOC 2, ISO 27001, etc.).
CCR™ score from 0 to 100 to measure observed evidence completeness.
Secuarden CLI
Price: Check official website
Local governance for AI-written code without requiring a cloud connection.
Offline verification of audit trail integrity.
AI-BOM (AI Bill of Materials) export to inventory AI systems.
Policy control enforcement via terminal commands.
Secuarden AI Screenshots
Secuarden AI alternatives
localscreenshot
localscreenshot is a screenshot API and MCP server for AI agents, returning clean captures of any web page on phone or desktop from 227 countries.
Nuclr Commander
Workspace for running multiple AI agents in parallel with a file manager. Supports local or external models and remote mobile monitoring.
SpeakCrate
Open-source API for local, private speech synthesis. Generate multilingual audio on your own servers with OpenAI standard compatibility.